소득공제
직수입양서
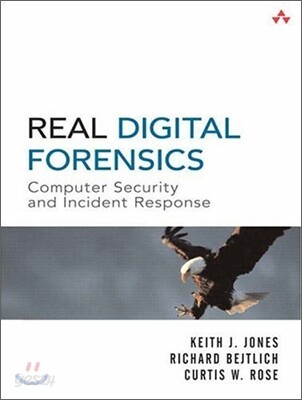
Real Digital Forensics: Computer Security and Incident Response [With DVD]
Computer Security and Incident Response
Paperback
Jones, Keith / Bejtlich, Richard / Rose, Curtis
Addison-Wesley Professional
2005.09.16.
이미 소장하고 있다면 판매해 보세요.
- 국내배송만 가능
- 문화비소득공제 가능
책소개
품목정보
- 발행일
- 2005년 09월 16일
- 쪽수, 무게, 크기
- 512쪽 | 크기확인중
- ISBN13
- 9780321240699
관련 자료
|
From the Back Cover
You can't succeed in the field of computer forensics without hands-on practice?and you can't get hands-on practice without real forensic data. The solution: Real Digital Forensics. In this book, a team of world-class computer forensics experts walks you through six detailed, highly realistic investigations and provides a DVD with all the data you need to follow along and practice. From binary memory dumps to log files, this DVD's intrusion data was generated by attacking live systems using the same tools and methods real-world attackers use. The evidence was then captured and analyzed using the same tools the authors employ in their own investigations. This book relies heavily on open source tools, so you can perform virtually every task without investing in any commercial software. You'll investigate environments ranging from financial institutions to software companies and crimes ranging from intellectual property theft to SEC violations. As you move step by step through each investigation, you'll discover practical techniques for overcoming the challenges forensics professionals face most often. Inside, you will find in-depth information on the following areas: Responding to live incidents in both Windows and Unix environments Determining whether an attack has actually occurred Assembling a toolkit you can take to the scene of a computer-related crime Analyzing volatile data, nonvolatile data, and files of unknown origin Safely performing and documenting forensic duplications Collecting and analyzing network-based evidence in Windows and Unix environments Reconstructing Web browsing, e-mail activity, and Windows Registry changes Tracing domain name ownership and the source of e-mails Duplicating and analyzing the contents of PDAs and flash memory devices The accompanying DVD contains several gigabytes of compressed data generated from actual intrusions. This data mirrors what analysts might find in real investigations and allows the reader to learn about forensic investigations in a realisticsetting. ⓒ Copyright Pearson Education. All rights reserved. |
사락 별점0
혜택 및 유의사항밑줄0
혜택 및 유의사항상품정보안내
직수입외서의 경우, 해외거래처에서 제공하는 정보가 부족하여 제목, 표지, 가격, 유통상태 등의 정보가 미비하거나 변경되는 경우가 있습니다. 정확한 확인을 원하시는 경우, 일대일 상담으로 문의하여 주시면 답변 드리겠습니다.
(판형과 판수 등이 다양한 도서는 찾으시는 도서의 ISBN을 알려 주시면 보다 빠르고 정확한 안내가 가능합니다.)
해외거래처에서 품절인 경우, 2차 거래선을 통해 유럽과 미국 출판사로 직접 수입이 진행될 수 있습니다.
수입 진행 시점으로 부터 2~3주가 추가로 소요되며, 해외에서도 유통이 원활하지 않은 도서는 품절 안내가 지연될 수 있습니다.
해당 경우, 문자와 메일로 별도 안내를 드리고 있사오니 마이페이지에서 휴대전화번호와 메일주소를 다시 한번 확인해주시기 바랍니다.
(판형과 판수 등이 다양한 도서는 찾으시는 도서의 ISBN을 알려 주시면 보다 빠르고 정확한 안내가 가능합니다.)
해외거래처에서 품절인 경우, 2차 거래선을 통해 유럽과 미국 출판사로 직접 수입이 진행될 수 있습니다.
수입 진행 시점으로 부터 2~3주가 추가로 소요되며, 해외에서도 유통이 원활하지 않은 도서는 품절 안내가 지연될 수 있습니다.
해당 경우, 문자와 메일로 별도 안내를 드리고 있사오니 마이페이지에서 휴대전화번호와 메일주소를 다시 한번 확인해주시기 바랍니다.
116,160원
총 1개
116,160원