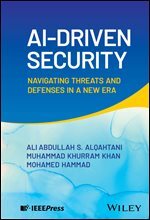
- PDF 안내
-
이 상품은 구매 후 지원 기기에서 예스24 eBook앱 설치 후 바로 이용 가능한 상품입니다.
소개
목차
|
1 Introduction: The Intersection of AI and Cybersecurity 1 1.1 Defining AI-Driven Security 2 1.1.1 Key Concepts in AI for Cybersecurity 2 1.1.2 How AI Differs from Traditional Methods 3 1.1.3 The Integration of AI in Cybersecurity 4 1.2 Historical Evolution of AI in Cybersecurity 6 1.2.1 Early Development (1990s–2000s) 7 1.2.2 Advancements in the 2000s 7 1.2.3 Modern AI-Driven Security (2010s–Present) 7 1.3 Why AI is a Double-Edged Sword 9 1.3.1 Opportunities: AI as a Defender 9 1.3.2 Threats: AI as an Adversary 10 1.4 Purpose and Scope of the Book 12 1.4.1 Who Should Read This Book 12 1.4.2 Overview of the Book Structure 12 1.5 Summary 14 I The Current State of AI in Cybersecurity 15 2 AI as a Defender 16 2.1 AI-Powered Threat Detection 17 2.1.1 Machine Learning and Anomaly Detection 18 2.1.2 Use Cases: AI in Intrusion Detection and Prevention Systems (IDPS) 22 2.2 AI in Endpoint Security 24 2.2.1 How AI Secures Endpoints Against Malware, Ransomware, and Zero-Day Exploits 24 2.2.2 Antivirus and Anti-Malware Solutions: The Role of AI 26 2.3 AI in Network Security 27 2.3.1 How AI Enhances Network Traffic Analysis and Detects Abnormalities in Real-Time 28 2.3.2 AI-Driven Solutions in Firewalls, Threat Intelligence, and Incident Response 29 2.4 Challenges and Future Directions for AI-Driven Defense Systems 31 2.4.1 Data Quality and Availability 31 2.4.2 Model Interpretability and Explainability 31 2.4.3 Adversarial Attacks on AI Systems 32 2.4.4 Future Directions for AI in Cybersecurity 32 3 AI as an Adversary 33 3.1 AI in Cyberattacks: Weaponization of AI 34 3.1.1 How Adversaries Use AI to Create Sophisticated, Autonomous Attack Systems 34 3.1.2 Case Studies: AI in Phishing, Malware, and Social Engineering Attacks 40 3.2 Deepfakes and Synthetic Media 41 3.2.1 The Rise of AI-Driven Disinformation Campaigns 42 3.2.2 Challenges Posed by Deepfakes in Fraud and Misinformation 44 3.2.3 Case Studies: Deepfakes in Fraud and Misinformation 45 3.3 Adversarial Machine Learning (AML) 45 3.3.1 Techniques Used by Attackers to Corrupt AI Models and Bypass Defenses 46 3.3.2 Examples of Adversarial Attacks: Poisoning, Evasion, and Model Inversion 48 3.4 Agentic AI: From Assistant to Autonomous Operator 49 3.4.1 Why Agency Changes the Threat Model 50 3.4.2 Agentic Jailbreaks and Task Decomposition 51 3.4.3 Case Study: The First AI-Orchestrated Espionage Campaign 51 3.5 Summary 52 II Emerging Threats in the AI Security Landscape 53 4 Adversarial AI: Attacks on AI Systems 54 4.1 Understanding Adversarial Inputs 56 4.1.1 How Attackers Manipulate AI Models Using Adversarial Inputs 56 4.1.2 Vulnerabilities in Image Recognition, Natural Language Processing (NLP), and Autonomous Systems 61 4.2 Real-World Case Studies of Adversarial Attacks 64 4.2.1 Examples of Successful Adversarial Attacks Across Industries 64 4.2.2 Exploring Consequences and Defensive Strategies 67 4.3 Summary 73 5 AI’s Role in Data Privacy and Security 74 5.1 Privacy Risks in AI-Driven Systems 75 5.1.1 Data Collection Challenges in AI Systems 75 5.1.2 Biases in AI Systems 80 5.1.3 Security Loopholes in AI Systems 82 5.2 Regulatory Frameworks and Their Impact on AI-Based Solutions 83 5.2.1 General Data Protection Regulation (GDPR) 83 5.2.2 California Consumer Privacy Act (CCPA) 84 5.3 AI in Privacy-Enhancing Technologies 85 5.3.1 Differential Privacy 86 5.3.2 Homomorphic Encryption 89 5.3.3 Federated Learning 92 5.4 How AI Can Protect User Privacy Without Sacrificing Security 96 5.4.1 Balancing Privacy and Utility in AI Systems 96 5.5 Summary 97 6 Generative AI and LLMs for Security 99 6.1 Applications of Generative AI in Security 100 6.1.1 Phishing Email Generation 100 6.1.2 Social Engineering Attacks 101 6.1.3 Malware Creation and Code Obfuscation 101 6.2 Security Challenges with Generative AI 103 6.2.1 Adversarial Use of Generative Models 103 6.2.2 Difficulty in Detecting AI-Generated Content 103 6.2.3 Proliferation of Misinformation via Deepfakes 104 6.3 Privacy Concerns in Generative AI 105 6.3.1 Inherent Privacy Risks in Training LLMs 105 6.3.2 Use of Sensitive Data in Model Training 105 6.3.3 Risks of Data Leakage from LLMs 106 6.4 Mitigation Strategies 107 6.4.1 Techniques to Secure Generative AI Models 107 6.4.2 Responsible Data Usage and Privacy-Preserving Mechanisms 108 6.4.3 Monitoring and Regulation of AI-Generated Content 109 6.5 Future Trends 109 6.5.1 Responsible Deployment of Generative AI 109 6.5.2 Advancements in Privacy-Enhancing Technologies for LLMs 110 6.6 Case Studies 110 6.6.1 Recent Security Incidents Involving Generative AI and LLMs 111 7 AI and Autonomous Systems Security 113 7.1 Security Challenges in AI-Driven Autonomous Systems 114 7.1.1 Securing AI in Autonomous Vehicles 114 7.1.2 Security in Autonomous Drones 119 7.1.3 Security in IoT Devices 122 7.2 AI in Robotics and Autonomous Agents 123 7.2.1 Security Measures for AI-Powered Robots 124 7.2.2 Defensive Strategies for Autonomous Systems Under Cyberattack 126 7.3 Summary 131 III Defenses and Mitigation Strategies for AI-Based Attacks 132 8 Defense Strategies Against AI-Driven Attacks 133 8.1 AI in Threat Intelligence and Prediction 134 8.1.1 How AI Predicts Future Attacks and Assists in Proactive Defense Strategies 134 8.1.2 Real-World Applications: Predictive Security Using AI 137 8.1.3 Benefits of AI-Driven Threat Intelligence 139 8.1.4 Challenges and Limitations of AI in Threat Intelligence 140 8.2 Reinforcement Learning in Defense Systems 142 8.2.1 How AI Learns to Autonomously Defend Against Cyberattacks in Dynamic Environments 142 8.2.2 Case Study: Self-Learning Defense Systems in High-Risk Industries 145 8.3 Zero Trust Architecture (ZTA) Enhanced by AI 147 8.3.1 Integrating AI into Zero Trust Models for Enhanced Security in a Perimeterless World 148 8.3.2 How AI Enables Continuous Verification and Dynamic Trust 151 8.3.3 Real-World Applications: Zero Trust Architecture Enhanced by AI 152 8.3.4 Benefits of AI-Enhanced Zero Trust Architecture 154 8.3.5 Challenges and Considerations in Integrating AI with ZTA 155 8.4 Securing Agentic AI Systems 156 8.4.1 The Expanded Attack Surface of Autonomous Agents 157 8.4.2 Non-Human Identity and Least-Privilege Access 157 8.4.3 Standards, Protocols, and Governance 158 8.5 Summary 159 9 Mitigating Adversarial Attacks on AI Systems 160 9.1 Building Robust AI Systems 161 9.1.1 Techniques to Harden AI Systems Against Adversarial Attacks 161 9.1.2 Best Practices in AI Model Development and Deployment 166 9.2 Ethical AI and Governance in Security 170 9.2.1 Importance of AI Ethics and Governance in Developing Secure AI Systems 171 9.2.2 Exploring Ethical Dilemmas in AI Use for Offensive and Defensive Purposes 175 9.3 Summary 177 10 AI-Assisted Incident Response and Forensics 179 10.1 AI’s Role in Automating Incident Response 180 10.1.1 How AI Accelerates Detection, Response, and Mitigation During Cyber Incidents 180 10.1.2 Use Cases of AI in Security Information and Event Management (SIEM) and Security Orchestration, Automation, and Response (SOAR) 185 10.2 AI in Digital Forensics 188 10.2.1 AI’s Application in Post-Breach Investigation and Data Recovery 189 10.2.2 How AI Helps Analyze Massive Datasets and Track Attacker Footprints 192 10.3 Summary 195 11 Defensive AI: Future Innovations and Roadmap 197 11.1 Advances in AI-Based Security Solutions 198 11.1.1 Future Innovations in AI-Based Defense Mechanisms 198 11.1.2 Exploring Next-Generation AI Solutions for Endpoint, Network, and Cloud Security 205 11.2 The Future of AI in Cybersecurity 209 11.2.1 What’s Next for AI-Driven Security? 209 11.2.2 Opportunities and Challenges for the Next Decade 212 11.3 Summary 216 IV Real-World Case Studies and Ethical Implications 217 12 Case Studies of AI-Driven Security Solutions 218 12.1 Industry Case Studies 219 12.1.1 Banking: AI-Enhanced Fraud Detection and Prevention 219 12.1.2 Healthcare: AI for Patient Data Protection and Threat Mitigation 221 12.1.3 Defense: AI for Military Network Security and Threat Intelligence 223 12.1.4 Critical Infrastructure: AI for Securing Power Grids and Industrial Control Systems (ICS) 226 12.2 Lessons Learned 228 12.2.1 What These Case Studies Teach Us About AI-Driven Security 228 12.2.2 Best Practices for Implementing AI-Driven Security Solutions 230 12.2.3 Pitfalls in AI-Driven Security Deployments 232 12.3 Summary 234 13 Ethical and Societal Implications 235 13.1 Balancing Security and Privacy 236 13.1.1 AI’s Role in Balancing Privacy Concerns with Security Needs 236 13.1.2 Societal Impacts of AI in Mass Surveillance and Intrusion240 13.2 AI for Good vs. AI for Evil 244 13.2.1 Ethical Dilemmas of Using AI in Offensive Cyber Operations 245 13.2.2 How to Ensure AI Is Used for Beneficial Purposes and Not Misused by Malicious Actors 248 13.3 Summary 251 14 Responsible and Ethical AI 252 14.1 Key Ethical Principles 253 14.1.1 Fairness 254 14.1.2 Transparency 255 14.1.3 Accountability 256 14.1.4 Data Privacy 258 14.2 Bias in AI Security Systems 259 14.2.1 How Bias Can Affect Security Outcomes 259 14.2.2 Examples of Biased AI Models in Security 260 14.2.3 Strategies to Reduce Bias in AI Systems 261 14.3 Regulatory Frameworks and Guidelines 262 14.3.1 General Data Protection Regulation (GDPR) 262 14.3.2 AI Ethics Frameworks 263 14.4 Best Practices for Building Responsible AI Systems 265 14.4.1 Human Oversight and Intervention 266 14.4.2 Continuous Monitoring and Updating AI Models 266 14.4.3 Ethical Governance Structures for AI in Security 266 14.5 Case Studies 267 14.5.1 Examples of Responsible AI in Cybersecurity 267 14.5.2 Pitfalls of Unethical AI Use in Security 268 14.6 Future Directions and Challenges 270 14.6.1 Advancements in Explainable AI 270 14.6.2 AI and International Security Policies 271 14.6.3 Ethical AI in Emerging Technologies 271 14.7 Summary 272 15 Conclusion: Navigating the AI-Driven Security Future 273 15.1 Key Takeaways from AI-Driven Security 274 15.1.1 Major AI-Driven Cyber Threats 274 15.1.2 AI-Enhanced Defenses Against Cyber Threats 277 15.1.3 Opportunities in AI-Driven Security 278 15.2 Building the Future of Secure AI Systems 280 15.2.1 AI’s Role in the Evolution of Cybersecurity 282 15.2.2 Addressing Challenges in AI-Driven Security 284 15.3 Call to Action for Researchers, Practitioners, and Policymakers 285 15.3.1 Priorities for Researchers 286 15.3.2 Best Practices for Security Practitioners 287 15.3.3 Recommendations for Policymakers 288 15.4 Conclusion 289 References 290 |
저자 소개
ALI ABDULLAH S. ALQAHTANI, PhD, is an Assistant Professor and Founding Director of the Defense Research Lab at Prince Sultan University, Riyadh, Saudi Arabia. His research advances zero-effort digital authentication, threat identification, IoT, AI, and ML. He has secured over $6.7M in funded grants as a Principal Investigator.
MUHAMMAD KHURRAM KHAN, PhD, is a global cybersecurity thought leader and Professor at King Saud University, Saudi Arabia. He is Founder and CEO of the Global Foundation for Cyber Studies and Research (USA), and Editor-in-Chief of Telecommunication Systems (Springer Nature). He has published over 500 research papers and holds 12 registered US patents.
MOHAMED HAMMAD, PhD, is an Associate Professor at Menoufia University, Egypt, and a Researcher at Prince Sultan University, Saudi Arabia. His work focuses on pattern recognition, AI, and cybersecurity. He has published 50+ SCI papers, edited five books, and is a top 2% cited scientist (Stanford, 2022?2025).
품목정보
- 발행일
- 2026년 11월 03일
- 지원기기
- 크레마, PC(윈도우 - 4K 모니터 미지원), 아이폰, 아이패드, 안드로이드폰, 안드로이드패드, PC(Mac)
- 파일/용량
- PDF(DRM) | 3.67MB ?
- 글자 수/ 페이지 수
- 약 225쪽 ?
- ISBN13
- 9781394371235
- ECN